|
| 1 | +## Summary |
| 2 | + |
| 3 | +Your setup is **primarily IaaS**, with some **PaaS-like behavior** that *you* are building yourself. You consume **SaaS** only for external tooling (e.g. GitHub). This is ideal for learning DevOps end-to-end. |
| 4 | + |
| 5 | +--- |
| 6 | + |
| 7 | +## Your current stack, mapped to IaaS / PaaS / SaaS |
| 8 | + |
| 9 | +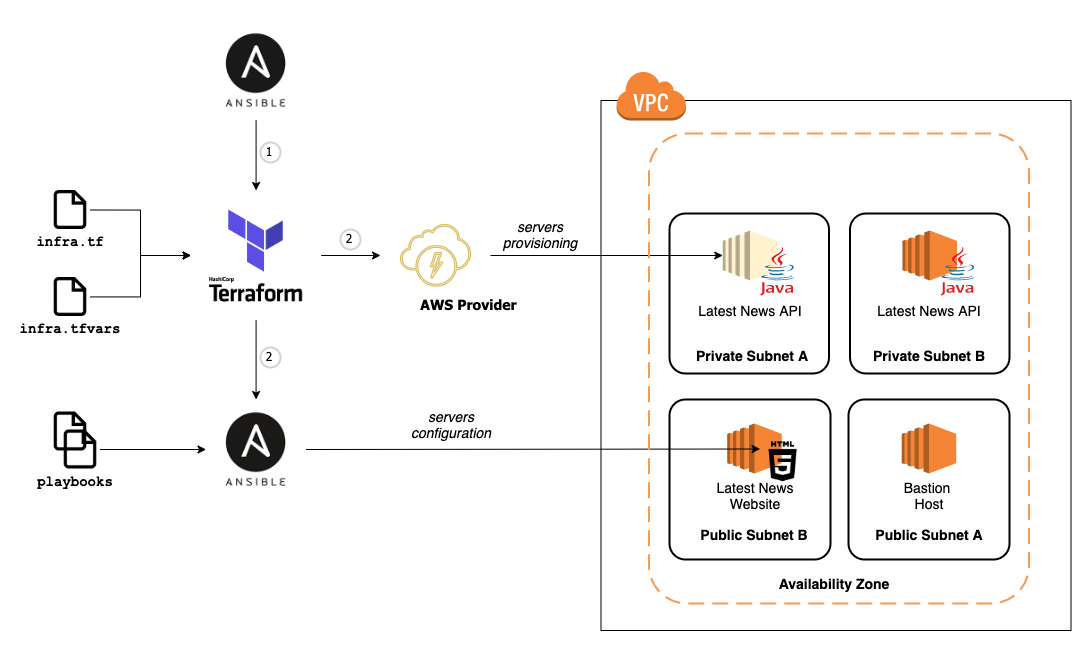 |
| 10 | + |
| 11 | + |
| 12 | + |
| 13 | + |
| 14 | + |
| 15 | +### 1. Infrastructure layer → **IaaS** |
| 16 | + |
| 17 | +**Terraform + Linode** |
| 18 | + |
| 19 | +What you control: |
| 20 | + |
| 21 | +* Virtual machines |
| 22 | +* Private networking |
| 23 | +* Firewalls |
| 24 | +* Public vs private IPs |
| 25 | + |
| 26 | +What the provider controls: |
| 27 | + |
| 28 | +* Physical servers |
| 29 | +* Data center |
| 30 | +* Hypervisor |
| 31 | + |
| 32 | +**Classification:** ✅ **IaaS** |
| 33 | + |
| 34 | +This is the foundation. Everything else runs *on top* of this. |
| 35 | + |
| 36 | +--- |
| 37 | + |
| 38 | +### 2. Server configuration → **Still IaaS** |
| 39 | + |
| 40 | +**Ansible** |
| 41 | + |
| 42 | +What you manage: |
| 43 | + |
| 44 | +* Users, SSH hardening |
| 45 | +* Docker installation |
| 46 | +* Fail2ban |
| 47 | +* Node Exporter |
| 48 | +* System updates |
| 49 | + |
| 50 | +Important insight: |
| 51 | + |
| 52 | +> Configuration management does **not** move you out of IaaS. |
| 53 | +
|
| 54 | +You are still managing: |
| 55 | + |
| 56 | +* The OS |
| 57 | +* Security |
| 58 | +* Services |
| 59 | +* Patching |
| 60 | + |
| 61 | +**Classification:** ✅ **IaaS (advanced, well-automated)** |
| 62 | + |
| 63 | +--- |
| 64 | + |
| 65 | +### 3. Application runtime → **Self-built PaaS** |
| 66 | + |
| 67 | +**Docker + Gunicorn + env vars** |
| 68 | + |
| 69 | +You’ve created: |
| 70 | + |
| 71 | +* A standard runtime |
| 72 | +* A repeatable deployment model |
| 73 | +* Environment-based configuration |
| 74 | +* Health endpoints |
| 75 | +* Metrics |
| 76 | + |
| 77 | +But: |
| 78 | + |
| 79 | +* You still manage the host |
| 80 | +* You still manage Docker |
| 81 | +* You still manage upgrades and failures |
| 82 | + |
| 83 | +This is the key DevOps insight: |
| 84 | + |
| 85 | +> You are **building a PaaS on top of IaaS**. |
| 86 | +
|
| 87 | +**Classification:** |
| 88 | + |
| 89 | +* Conceptually → **PaaS** |
| 90 | +* Practically → **IaaS with a platform layer** |
| 91 | + |
| 92 | +This is exactly how many real platforms started (Heroku included). |
| 93 | + |
| 94 | +--- |
| 95 | + |
| 96 | +### 4. CI/CD & tooling → **SaaS** |
| 97 | + |
| 98 | +**GitHub, GitHub Actions** |
| 99 | + |
| 100 | +What you *don’t* manage: |
| 101 | + |
| 102 | +* Build servers |
| 103 | +* Runners |
| 104 | +* Scaling |
| 105 | +* Availability |
| 106 | + |
| 107 | +You just: |
| 108 | + |
| 109 | +* Push code |
| 110 | +* Configure workflows |
| 111 | +* Consume the service |
| 112 | + |
| 113 | +**Classification:** ✅ **SaaS** |
| 114 | + |
| 115 | +--- |
| 116 | + |
| 117 | +## Responsibility breakdown (your exact setup) |
| 118 | + |
| 119 | +| Layer | Example | Model | |
| 120 | +| ----------------- | ----------------------- | ---------------------- | |
| 121 | +| Hardware | Linode data center | SaaS (hidden from you) | |
| 122 | +| VM / Network | Terraform | IaaS | |
| 123 | +| OS & Security | Ansible | IaaS | |
| 124 | +| Container runtime | Docker | IaaS | |
| 125 | +| App platform | Your Docker conventions | DIY PaaS | |
| 126 | +| App code | Flask / Gunicorn | PaaS responsibility | |
| 127 | +| CI/CD | GitHub Actions | SaaS | |
| 128 | +| Monitoring UI | Grafana Cloud (if used) | SaaS | |
| 129 | + |
| 130 | +--- |
| 131 | + |
| 132 | +## Why this is an excellent DevOps learning path |
| 133 | + |
| 134 | +You are learning **all responsibility boundaries**, not just one: |
| 135 | + |
| 136 | +* **IaaS** → networking, firewalls, SSH, Linux |
| 137 | +* **PaaS concepts** → runtime standardization, config via env vars |
| 138 | +* **SaaS consumption** → CI/CD, observability platforms |
| 139 | + |
| 140 | +Many DevOps engineers: |
| 141 | + |
| 142 | +* Use PaaS without understanding IaaS |
| 143 | +* Or manage IaaS without understanding platform design |
| 144 | + |
| 145 | +You’re doing **both**, in the correct order. |
| 146 | + |
| 147 | +--- |
| 148 | + |
| 149 | +## Real-world analogy (extended) |
| 150 | + |
| 151 | +* **Linode + Terraform** → You bought land |
| 152 | +* **Ansible** → You built the house and utilities |
| 153 | +* **Docker runtime** → You standardized apartments |
| 154 | +* **Your app** → Tenants move in |
| 155 | +* **GitHub Actions** → External cleaning & maintenance service |
| 156 | + |
| 157 | +--- |
| 158 | + |
| 159 | +## What your *next step* could be (optional) |
| 160 | + |
| 161 | +If you want to *move slightly toward PaaS without losing learning value*: |
| 162 | + |
| 163 | +* Add **automatic app restarts** |
| 164 | +* Add **zero-downtime deploys** |
| 165 | +* Add **service discovery / reverse proxy rules** |
| 166 | +* Treat each app as cattle, not pets |
| 167 | + |
| 168 | +That would make your setup: |
| 169 | + |
| 170 | +> **A minimal, production-style PaaS built on IaaS** |
| 171 | +
|
| 172 | +If you want, next we can: |
| 173 | + |
| 174 | +* Redraw this as a **single architecture diagram** |
| 175 | +* Or map this directly to **AWS equivalents** (EC2, ECS, EKS, Elastic Beanstalk) |
| 176 | + |

0 commit comments